| Product Documentation
AD Connect Sync
Enabling LDAPS Self-Signed Certificates
By default Microsoft Active Directory servers are unsecured. This means all LDAP messages are passed over unencrypted connections and in clear text. Some cases require that usernames and password modifications are performed over a secure channel such as SSL. To enable LDAP over SSL i.e. LDAPS you would need to install an SSL certificate on the Domain Controller. This article explains how to secure Cloud Domain Controller with a self-signed certificate.
- Access the Cloud DC machine open Server Manager and select option “Add roles and Features”

- Enable option “Active Directory Certificate Services”
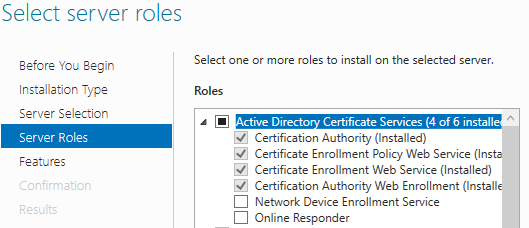
Press next for next couple of pages and then enable following options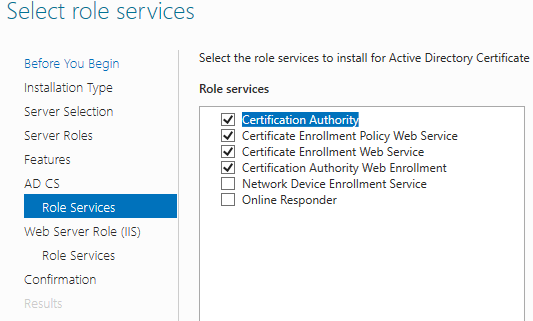
Continue pressing next with default setting and click finish at the end - Once installation completed click on “Configure Active Directory Certificate Services on the destination server”
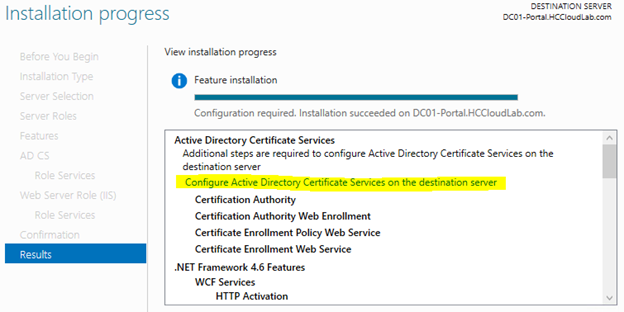
- Select following option in “Role Services”
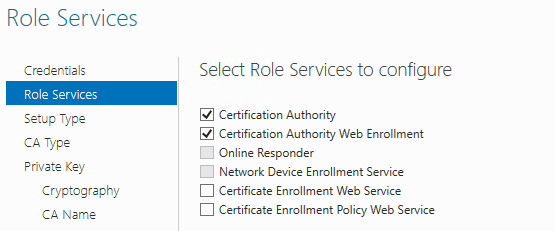
On next screen select “Enterprise CA”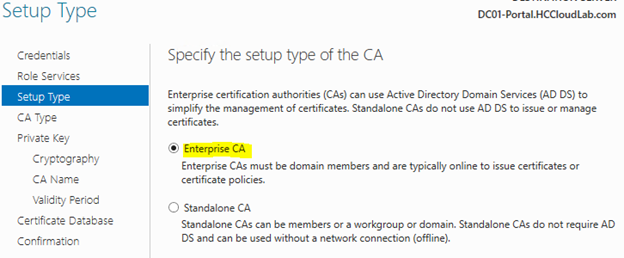
Select “Root CA”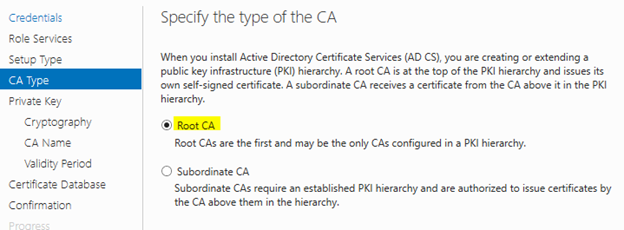
Select “Create a new Private Key”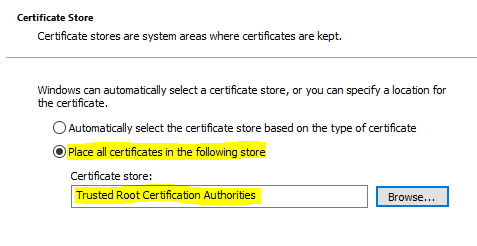
On next screen select option “Allow administrator interaction when the private key is accessed by the CA"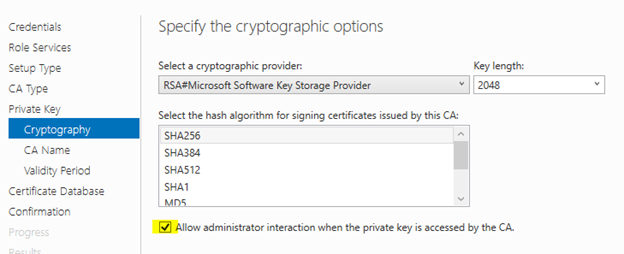
- Continue pressing next to select default values and complete the configuration
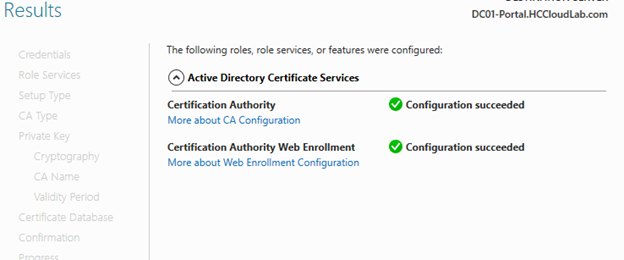
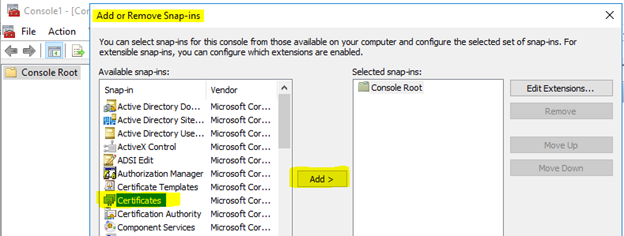
- To see the certificate in the system open command prompt and type “mmc”, a console will open select “File > Add or Remove Snap-ins” and select “Certificate” and click Add button
On next screen select “Computer Account”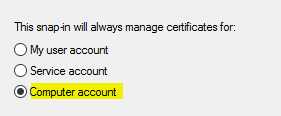
You can see installed certificate in “Personal”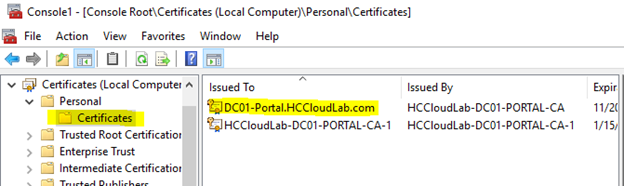
- Export Certificate
Right click on the certificate name > All Tasks >> Export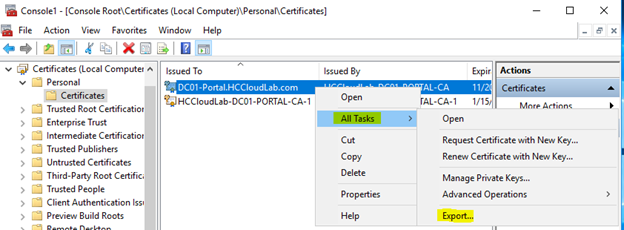
Select the default values on next screens and complete the process. - Import certificate
First move the certificate which you have exported in step 7 on client machine. Right click on the certificate and select “Install Certificate”, and select following options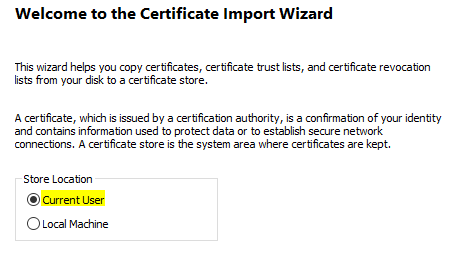
Place certificate in “Personal” Folder and complete the process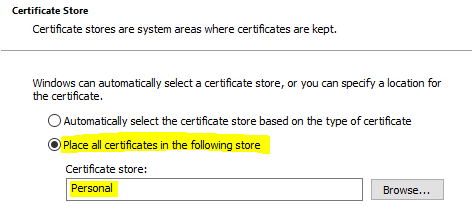
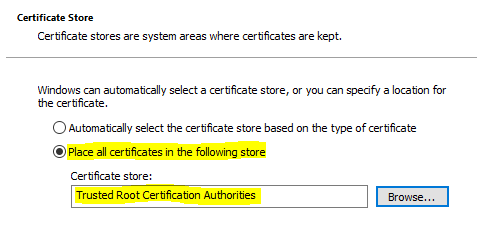
Again follow step 8 from above and this time place certificate in “Trusted Root Certification Authorities"