| Product Documentation
AD Connect Sync
How it Works
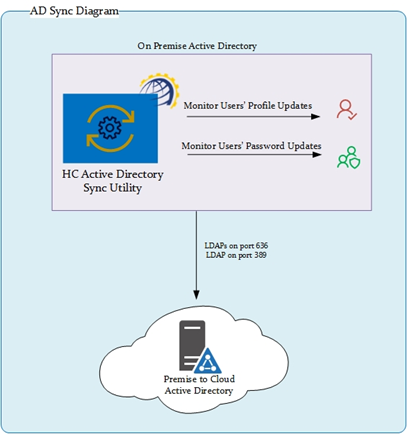
HC ADSync Tool is developed as a simple windows service “HCdirSync”. This service is deployed onto domain controller in the on-premises AD forest. As changes are made in the on-premises domains, the changes are replicated to the cloud environment using direct LDAP communication.
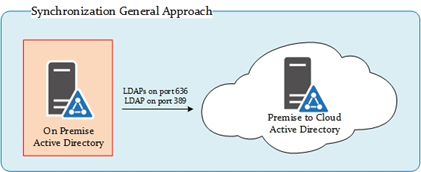
The ongoing user object identity information (properties and attributes) are synchronized. On-premise password changes are intercepted and replicated through HC ADSync to associated user object in the private/public cloud. Newly created user accounts on the on-premises domains are synchronized. Deletion of an on-premises user object will result in deletion of the user object and its assigned service offerings in the private/public cloud. Resource mailboxes are treated in a similar concept as user objects.
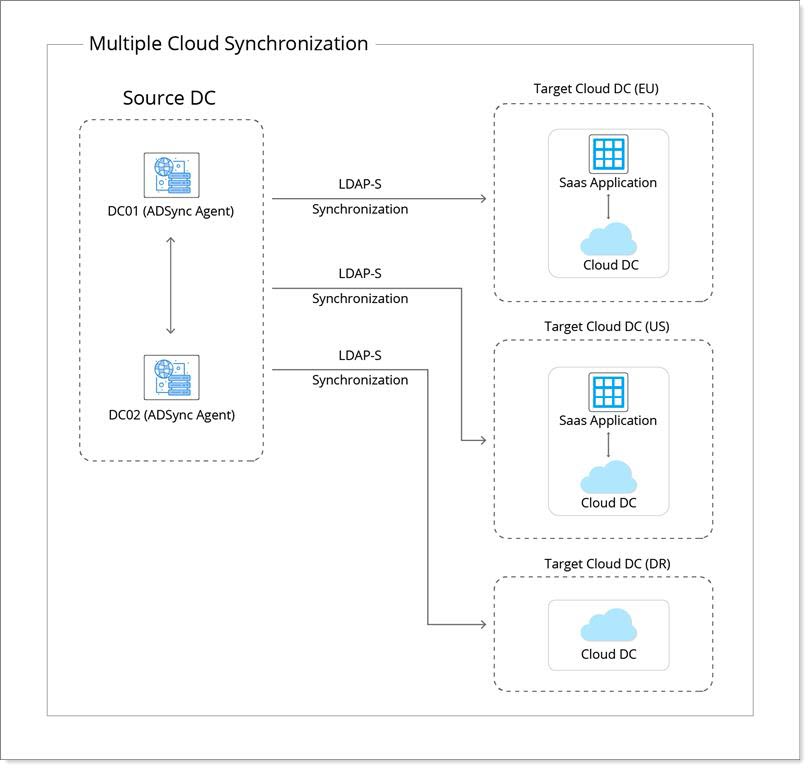
The ADSync Tool can also synchronize users from a single on-premises AD to multiple cloud ADs. Each independent cloud AD can have its own settings. You may also specify some objects of an OU to be synchronized with one cloud AD and some with another. Even a single user can be synchronized with more than one cloud ADs simultaneously.
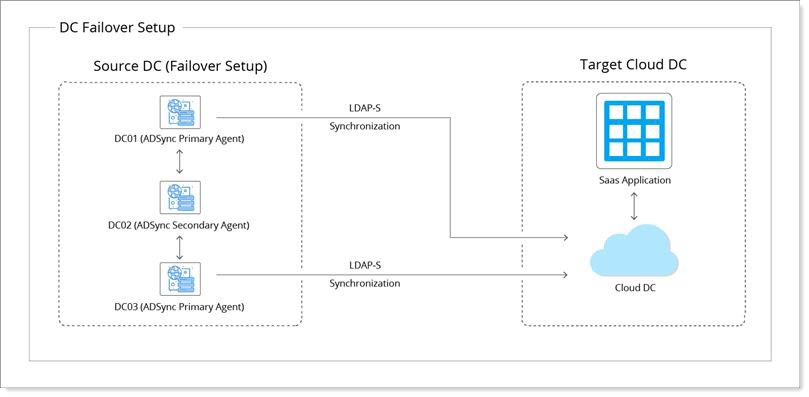
ADSync Tool can also be configured for high availability (H.A). The AD Sync Primary Agent can be installed on two or more source Domain Controllers for this purpose. This redundancy ensures that if one source DC becomes unavailable, AD synchronization will continue unabated from the second source Domain Controller.